AZURE OPERATIONS · BUILT WITH OVERLIFT

Azure Cloud Portal

Bring the application’s health into one view.

Azure Cloud Portal brings resource information, health, and telemetry into an operating view. The case study shows how cached status and identity-aware controls can help an operator investigate a problem and review a proposed fix.
See the operations workflow See the evidence
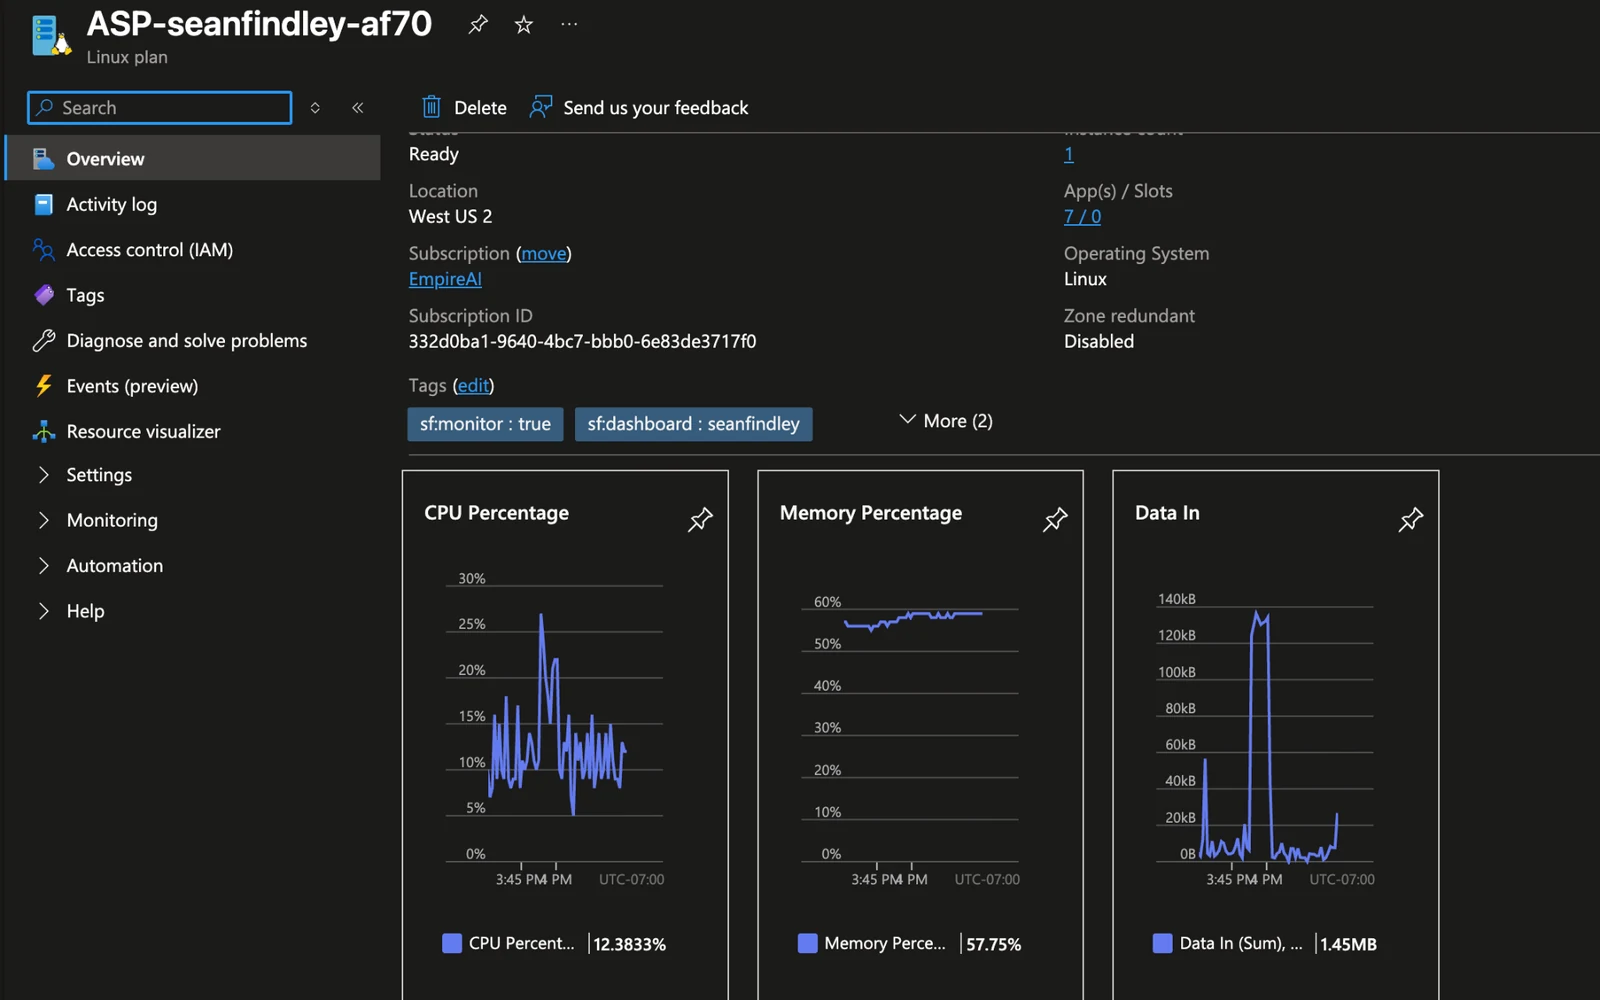
Azure App Service operations overview with resource identity, CPU, memory, and network telemetry
Azure operations view A real Azure operations surface connects application identity, resource state, and live telemetry—the evidence boundary the Cloud Portal turns into a guided operational workflow.

Recorded project scope

Delivery status is not specified in this case study.

MARKETING

Who it helps and why.

A cloud incident rarely arrives as one clean error. The symptom may appear in an application while the cause sits in identity, networking, configuration, a dependency, a deployment, or a data service. Operators lose time moving between portals and can make a risky change before they understand the complete state.

What makes it useful: Traditional portals expose many dashboards but leave the operator to reconcile them mentally. This system connects telemetry, dependencies, deployment history, policy, and authority into one typed state, then compares remediation paths without granting an AI unrestricted cloud control.

BUSINESS / EXECUTIVE

Business value.

The intended benefit is less time switching between operational views when investigating an application. Incident resolution time and production reliability need to be measured in the actual deployment.

Explore the business outcomes
  • Faster operational visibility
  • Stronger DevOps story
  • Better proof of production-minded engineering
ARCHITECTURE

How the system fits together.

The AI value is not a chatbot bolted onto a dashboard. It is the operating foundation around AI-enabled apps: fast cached status, diagnostics, telemetry, inventory, security-aware access patterns, and the kind of cloud visibility an applied-AI product needs before it can be trusted in production.

A representative workflow

  1. 01

    Choose an application or resource and inspect its health, configuration, and recent activity.

  2. 02

    Compare the relevant telemetry and dependencies, noting stale or missing information.

  3. 03

    Review a proposed change with the responsible operator and verify the resulting state through the deployment’s controls.

Explore the architecture details

I built an Azure-backed operational control plane that brings application health, resource inventory, telemetry, cached status, Redis, PostgreSQL, configuration, and deployment-oriented workflows into one fast administrative surface. The design separates observation, diagnosis, proposal, authorization, and verification instead of treating every alert like an invitation to click a button.

ENGINEERING

Engineering choices.

I used cached operational views to bring resource identity, health, and telemetry together. The interface keeps the evidence behind a suspected cause visible so an operator can review a change through the appropriate identity and approval controls.

Explore the technology and engineering details
Technology stackASP.NET Core, Azure, Azure Monitor, Redis, PostgreSQL, OAuth 2.0, Microsoft Entra ID
  • Cached dashboard and configuration surfaces for rapid iteration
  • Azure Monitor and telemetry-oriented operational views
  • Redis/PostgreSQL visibility and deployment-aware workflows
OVERLIFT METHOD

How this product applies the OverLift method.

The OverLift method turns scattered cloud metrics, dependencies, identities, policies, and deployment facts into one typed operational state. It can compare diagnostic and remediation paths, reject steps that break permission, policy, cost, or rollback rules, and preserve a receipt showing why the recommended route was safer than the alternatives.

Explore the shared OverLift architecture

The method is reusable. Each product supplies its own facts, rules, execution, and validation. These tiers describe the shared architecture; the project scope above records which capabilities are implemented here.

Why determinism matters here: Cloud state changes quickly and actions can be expensive. Determinism keeps diagnosis, authority, execution, and verification tied to a known resource and deployment state.

  1. T0
    Exact baseline

    Define the authoritative result before adding acceleration, semantics, or agents.

  2. T1
    Measured evidence

    Instrument state, latency, quality, and failure so improvement is observable.

  3. T2
    Bounded ownership

    Move expensive or high-frequency work behind clear worker and memory boundaries.

  4. T3
    Deterministic transport

    Version messages, snapshots, identities, deadlines, and replay inputs.

  5. T4
    Semantic assistance

    Let local retrieval and models propose meaning only inside admitted evidence.

  6. T5
    Candidate paths

    Compare several allowed next actions with explicit risk, cost, fit, and uncertainty.

  7. T6
    Shadow verification

    Challenge the production route without giving the challenger authority.

  8. T7
    Governed production

    Promote only measured, replayable paths with fallback and operational receipts.

  9. Tier-S
    Experimental challenger

    Run advanced evaluators in shadow, compare them with the control, and graduate only repeatable gains.

CATS

Context-Aware Tier Selection

CATS chooses a qualified execution tier for the evidence, device, latency, permissions, and failure conditions of the task.

SEMANTIC BRIDGE

Meaning becomes typed product state

The Semantic Bridge maps a goal to explicit entities, evidence, uncertainty, tools, and permissions. Missing or contradictory information remains visible.

DETERMINISM

Validate the action and retain the result

Models may retrieve, compare, or propose. Exact software checks facts, permissions, state changes, and execution, then records what happened.

OverLift securityAgentic AI Glossary

Read the OverLift MethodOverLift.ai See other products
PROOF

Evidence and limits.

The case study includes an Azure operations view and describes how resource state and telemetry support an investigation. It does not demonstrate autonomous remediation or establish availability and recovery guarantees for an entire subscription.

Back to the project overview ↑